
KMRA CONDUCTS ISO/IEC 27001:2022 CERTIFICATION AUDIT AT GREYSTONE DATA SYSTEMS
KMRA Conducts ISO/IEC 27001:2022 Certification Audit at GREYSTONE DATA SYSTEMS, a Developer of AI, Software and Automation Solutions
KMRA – KM Registrar & Assurance conducted an ISO/IEC 27001:2022 certification audit at GREYSTONE DATA SYSTEMS, a company specialising in artificial intelligence (AI), software development and automation. The audit demonstrates KMRA’s professional expertise in information security management system certification for high-tech businesses.
What Is ISO 27001 Certification?
ISO 27001 certification is an independent assessment process designed to verify whether an organisation’s Information Security Management System (ISMS) conforms to the requirements of the international standard ISO/IEC 27001.
ISO/IEC 27001:2022 specifies requirements for establishing, implementing, maintaining and continually improving an Information Security Management System, enabling organisations to manage risks and protect their information assets.
Implementing an ISMS and achieving ISO 27001 certification offer several benefits to organisations:
- Enhancing the protection of data, customer information and technological assets.
- Identifying, assessing and managing information security risks.
- Strengthening governance capabilities and business continuity.
- Meeting information security requirements set by customers and business partners.
- Enhancing corporate credibility and competitive advantage in international supply chains.
For businesses operating in information technology, artificial intelligence and automation, ISO 27001 plays a vital role in establishing a secure, systematic information management environment aligned with international best practices.
KMRA Conducts ISO/IEC 27001:2022 Certification Audit at GREYSTONE DATA SYSTEMS
As part of its management system certification activities, KMRA conducted an ISO/IEC 27001:2022 certification audit at GREYSTONE DATA SYSTEMS.
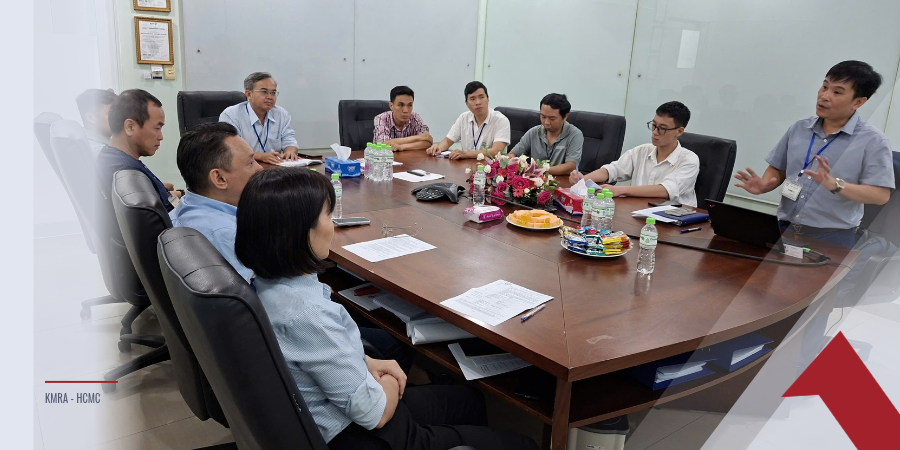
KMRA Conducts ISO/IEC 27001:2022 Certification Audit at GREYSTONE DATA SYSTEMS
GREYSTONE DATA SYSTEMS operates in the following fields:
The design, development, integration and provision of artificial intelligence (AI) solutions for detecting functional and cosmetic defects in mobile devices, as well as software for operating automated, semi-automated equipment and robotic systems.
These fields involve stringent requirements for data management, intellectual property protection, access control and information security throughout the development, integration and operation of technology solutions.
During the audit, the KMRA audit team assessed the organisation’s Information Security Management System (ISMS) against the requirements of ISO/IEC 27001:2022. The assessment involved personnel interviews, document reviews and verification of objective evidence of implementation in practice.
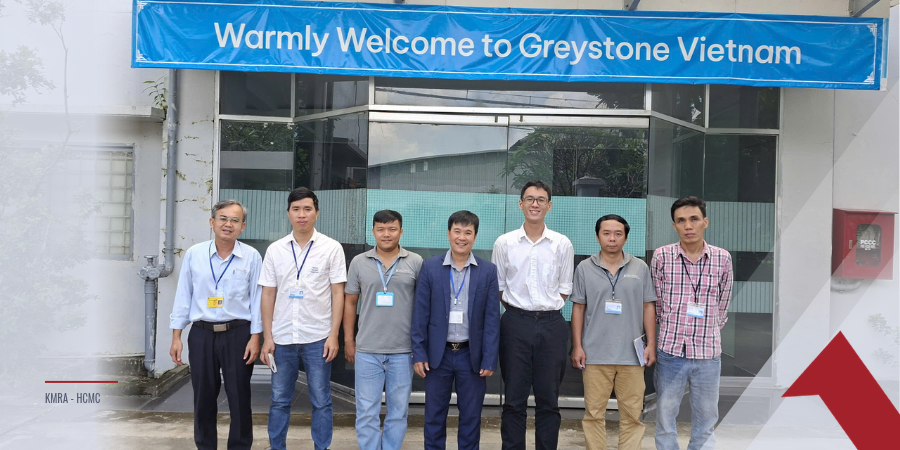
KMRA ISO/IEC 27001 Certification Audit Team and GREYSTONE Representatives
The audit was conducted using a risk-based approach to determine the conformity and effectiveness of the Information Security Management System within the scope of the assessment.
Key Focus Areas of the ISO/IEC 27001:2022 Certification Audit
For businesses developing AI solutions, software and automation systems, such as GREYSTONE DATA SYSTEMS, the ISO 27001 certification audit focuses on key aspects of information management and protection throughout their operations.
The main areas of assessment include:
1. Information Security Risk Management
Reviewing the methods used to identify, analyse, assess and treat risks associated with data, software systems and technology operations.
2. Protection of Data and Information Assets
Assessing the management, classification and protection of information, including customer data, technical documentation, software source code and other relevant information assets.
3. Access Control and System Security
Reviewing measures for managing access rights, user authentication and protecting information systems against unauthorised access.
4. Information Security in Software Development
Assessing the integration of information security requirements into software design, development, testing, deployment and maintenance activities.
5. Incident Management and Business Continuity
Reviewing the organisation’s ability to detect, respond to and recover from information security incidents, as well as maintain the operation of critical systems.
Through the assessment of these relevant requirements, the certification body can determine the extent to which the organisation’s Information Security Management System conforms to ISO/IEC 27001:2022.
KMRA Strengthens ISO 27001 Certification Capabilities for High-Tech Businesses
The development of artificial intelligence, digital technologies and automation systems is creating increasingly stringent requirements for information security management in businesses.
In response to this trend, KMRA – KM Registrar & Assurance continues to strengthen its capabilities in conducting certification audits of management systems against international standards, including ISO/IEC 27001:2022.
KMRA Audit Team Conducts ISO/IEC 27001 Certification Audit at GREYSTONE DATA SYSTEMS
The certification audit programme at GREYSTONE DATA SYSTEMS provides a practical demonstration of KMRA’s capability to conduct audits for organisations operating in specialised fields, including:
- Information technology and software development.
- Artificial intelligence (AI) and digital technology solutions.
- Electronics and telecommunications equipment.
- Automation systems and robotics.
- Technology solutions for industrial manufacturing.
With a commitment to professionalism, independence and international integration, KMRA focuses on strengthening auditor competence, complying with applicable certification requirements and developing international cooperation.
Which Businesses Should Obtain ISO 27001 Certification?
ISO 27001 certification is suitable for organisations seeking to establish an Information Security Management System (ISMS), particularly those that regularly process data, develop software or provide technology solutions.
The following types of organisations may consider implementing ISO/IEC 27001:2022:
- Information technology and software companies.
- Artificial intelligence and AI solution developers.
- Electronics and telecommunications companies.
- Automation and robotics solution providers.
- Cloud computing, data and technology infrastructure service providers.
- Organisations required to meet information security requirements set by international customers and business partners.
The scope of ISO 27001 certification should be determined based on each organisation’s actual operations, management system boundaries, information assets and associated risks.
Frequently Asked Questions About ISO 27001 Certification
What is ISO 27001:2022 about?
ISO/IEC 27001:2022 is an international standard specifying requirements for an Information Security Management System (ISMS). It helps organisations manage risks and protect the confidentiality, integrity and availability of information.
Do software and AI development companies need ISO 27001 certification?
ISO 27001 certification is not mandatory for all software and AI development companies. However, the standard is particularly beneficial for organisations that need to protect data, manage information security risks and meet the requirements of customers and business partners.
Is ISO 27001 certification internationally recognised?
ISO 27001 certification can be issued under an international accreditation framework when the certification body and certification scope meet the relevant accreditation requirements. Organisations should verify the certification body, accreditation scope and accreditation validity to determine the recognition status of the certificate.
KMRA – Your Certification Partner for Management Systems
KMRA – KM Registrar & Assurance provides management system certification audit services against international standards, with a focus on impartiality, professional competence and long-term value for clients.
Through the ISO/IEC 27001:2022 certification audit at GREYSTONE DATA SYSTEMS, KMRA continues to expand its audit experience in the high-tech sector, supporting businesses in strengthening their information security management capabilities.
Organisations interested in ISO/IEC 27001:2022 certification are welcome to contact KMRA for further information on the certification scope, process and services best suited to their needs.
If you wish to register for ISO certification or training, or require advice on selecting the most suitable standard, please contact KMRA for assistance and a detailed quotation.
KMRA provides guidance on the certification process, audit scope, implementation timeline, and costs tailored to each organization's size and field of operation.
KMR VIETNAM COMPANY LIMITED
Ho Chi Minh City Head Office: ☎︎ +84 28 3535 4350 | Zalo: 0983 890 712 | support@kmra.vn
Hanoi Branch: ☎︎ Zalo: 0966 177 712 | support@kmra.vn
KMRA ACADEMY: ☎︎ Zalo: 0982 704 713 | cs002@kmra.vn
main.comment_read_more